IT Contingency Plan
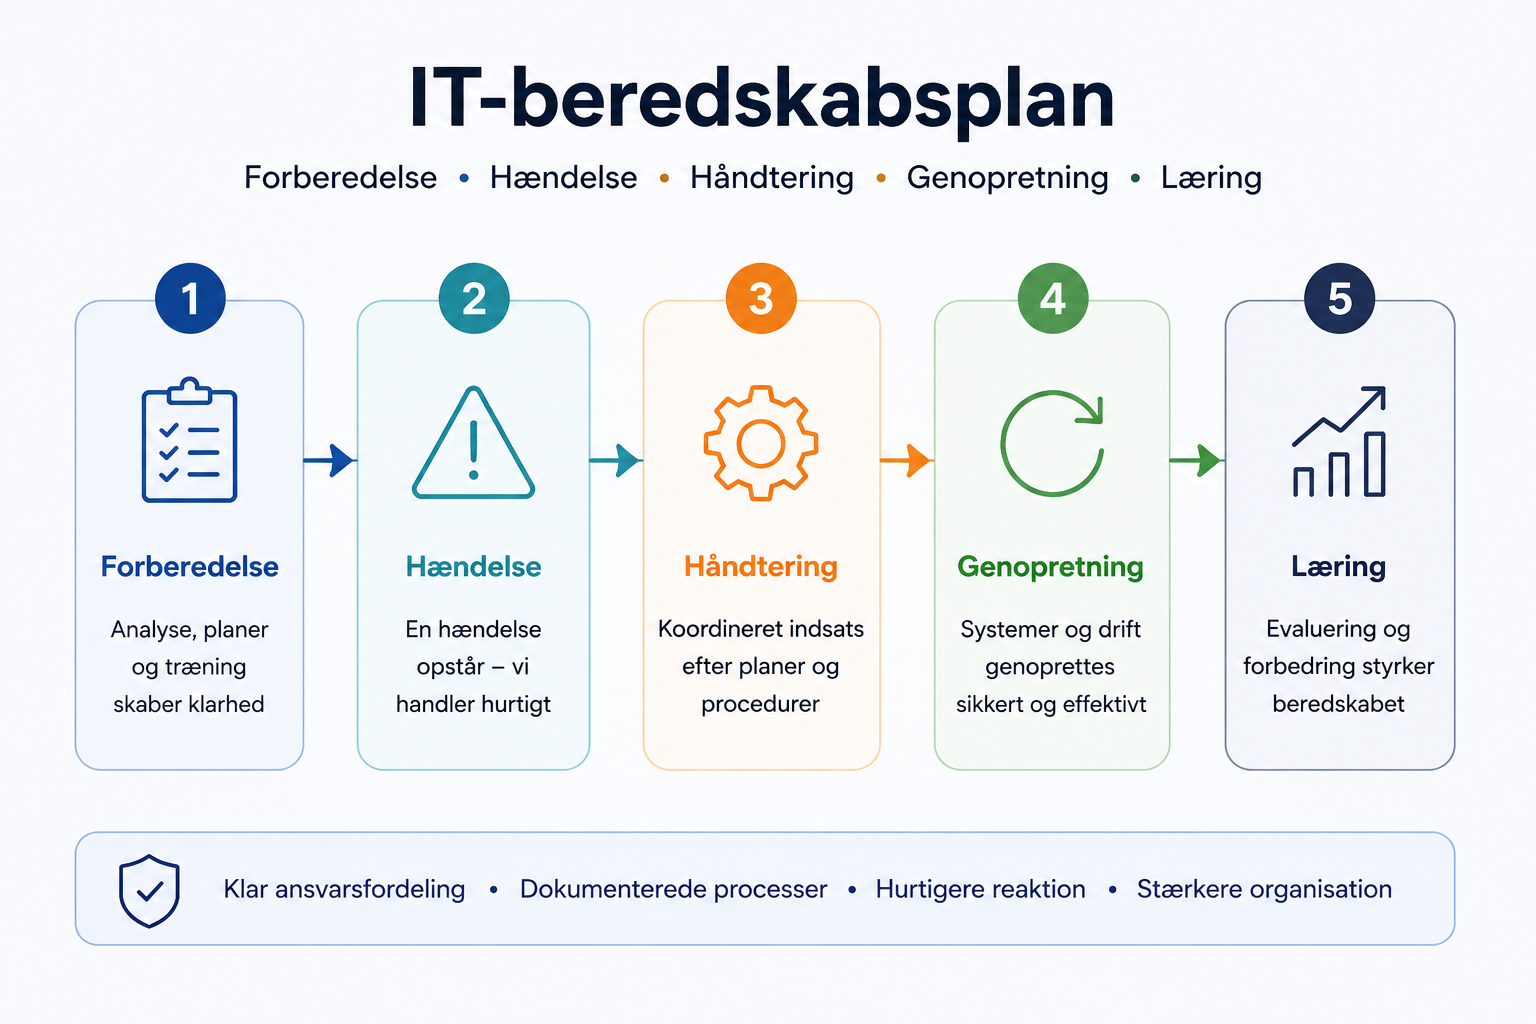
Cyber incidents can affect an organization’s operations, data, and ability to deliver critical services. For many organizations, the challenge is not only to prevent incidents but also to have a clear plan for how to handle them when they occur.
An IT contingency plan provides you with clearly defined roles, specific procedures, and a documented basis for rapid response and recovery. We help you create a practical and actionable plan that strengthens your organization’s resilience and supports requirements for contingency planning, incident management, and business continuity.
IT Contingency Plans: From Plan to Action
Step 1
Organization
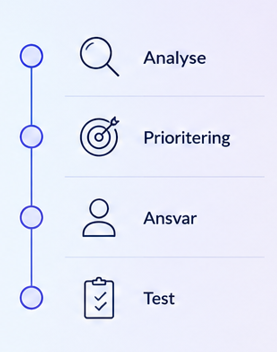
The IT contingency plan must be tailored to each company’s systems, employees, workflows, and structure. Therefore, rather than implementing a generic plan directly, companies should use a template as a starting point and adapt it to their specific needs. The first step is to create an overview of the company’s critical assets and business processes.
Step 2
IT incident
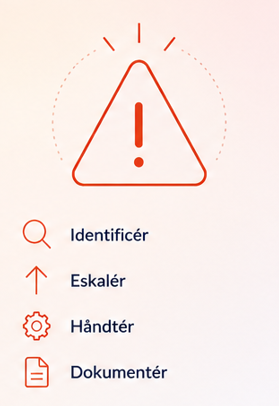
An IT contingency plan describes how the company should respond when a critical IT incident occurs. This could include ransomware, system failures, data breaches, cyberattacks, or other incidents that affect operations, data, and business-critical processes.
The purpose is simple: to ensure that the company can act quickly, in a structured and coordinated manner, when the situation requires it.
Step 3
IT Downtime
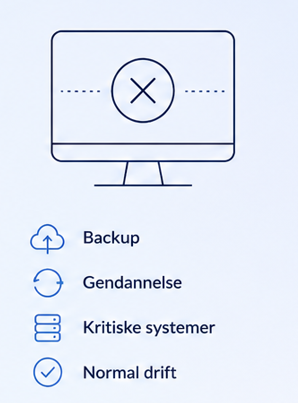
Many companies today are heavily reliant on their IT systems. As a result, downtime, data loss, or a lack of visibility in a critical situation can quickly become a business-critical issue.
Without a clear contingency plan, it can be difficult to coordinate efforts, make the right decisions, and communicate effectively with employees, customers, suppliers, and authorities. This can exacerbate the consequences and prolong the time it takes for the company to return to normal operations.
Step 4
Development of the Plan
A robust IT contingency plan should, among other things, describe:
- Roles and Responsibilities in the Event of Security Incidents.
- Communication and Escalation Procedures.
- Backup and recovery processes.
- Handling Operational Disruptions.
- Prioritization of critical systems, processes, and assets.
- Testing, learning, and continuous improvement.
When responsibilities, procedures, and decision-making processes are defined in advance, it becomes easier to limit the consequences of an incident, reduce downtime, and protect the company’s data, systems, and reputation.
Step 5
Education
Studies show that about 95% of all successful cyberattacks are due to human error. Therefore, it is not enough to simply have an IT contingency plan on paper; rather, the plan must be tested and practiced on an ongoing basis. We can advise and guide you on how to test and practice your IT contingency plan.

Step 6
Full compliance:
We can help you develop and implement an IT contingency plan based on current legislation and relevant requirements, so your company can demonstrate compliance and reduce the risk of fines, orders, and regulatory consequences.
IT Contingency Plan - Complete Package
Contact us for ad hoc consulting at
or start with our preliminary analysis.
Consulting and Plan Development
Practical and useful, tailored to the needs of each individual organization
Contents
Mapping of Risks, Dependencies, and Business-Critical Processes
Allocation of Roles, Responsibilities, and Escalation Paths
Procedures for Handling Cyber Incidents and System Outages
Backup and Recovery Procedures
Communication Plan – for Security Incidents and System Failures
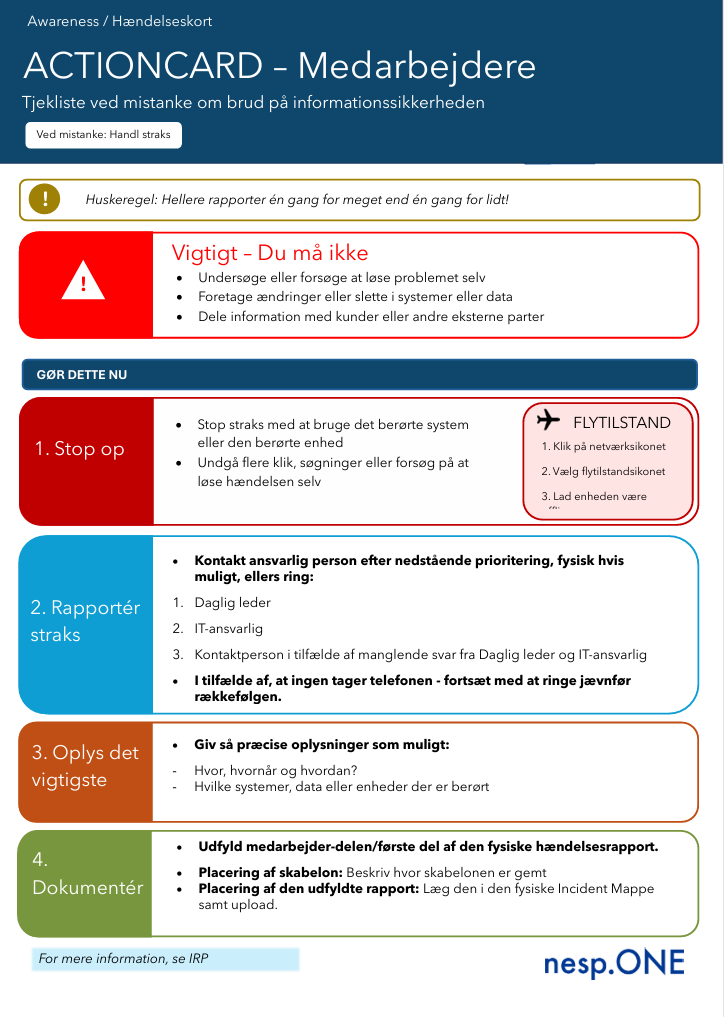
Action cards with specific actions for selected events
Documentation that can support requirements in, for example, NIS2 and ISO 27001
Expected output
A Concrete and Practical IT Contingency Plan
Clear Division of Responsibilities in the Event of Security Incidents
Faster response and recovery in the event of a system failure or cyberattack
Increased safety awareness among employees
Increased trust among customers, business partners, and government agencies
Start with a no-obligation consultation with one of our experts, or purchase a customized contingency plan starting at 5,000 DKK
The First Step Toward a Functional IT Contingency Plan
Send us an email to schedule a free 15-minute consultation on contingency planning with one of our cybersecurity experts.
View upcoming courses and webinars
Learn how your company can strengthen cybersecurity and achieve compliance with standards such as ISO 27001, NIS2, and CRA.
NIS2 for management
København / 11.11.26
NIS 2 in Practice
København / 12-13.11.26
ISO 27001: Certificate Course
København / 25-26.11.26
NIS2 for management
København / 19.01.27